MeitY introduces Data Empowerment and Protection Architecture (DEPA) for AI Training
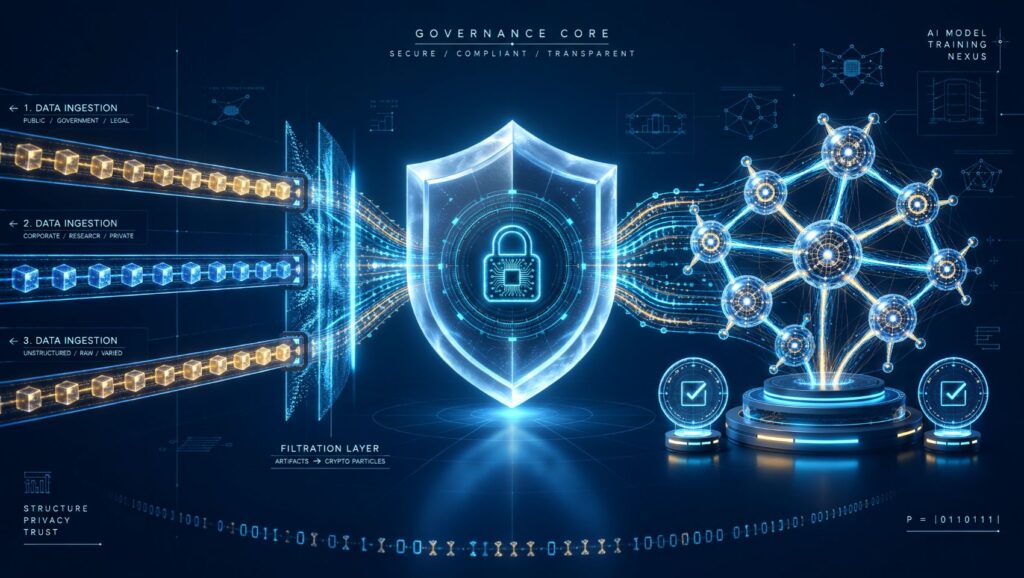
The Ministry of Electronics and Information Technology (“MeitY”), Government of India, has introduced the Data Empowerment and Protection Architecture for AI Training (“DEPA Framework”) to facilitate secure, privacy-preserving and accountable data sharing for Artificial Intelligence (“AI”) model training. The DEPA Framework establishes a techno-legal architecture for enabling collaboration between institutions holding datasets and organisations developing AI models. It provides for the use of Data Exchange Platforms, Electronic Contracts, Secure Data Environments and Differential Privacy mechanisms to facilitate responsible data sharing while safeguarding personal data, commercial confidentiality and data security.
The framework is based on the principles of Accountability, Democratization, Evolvability, Privacy, Transparency and Security (“ADEPTS”) and aligns data-sharing and AI training practices with applicable legal requirements, including the Digital Personal Data Protection Act, 2023.
Key Highlights:
- A structured mechanism for data sharing between institutions and AI developers has been established. The framework identifies Training Data Providers (“TDPs”), such as hospitals, financial institutions, pharmaceutical companies and public agencies holding datasets, and Training Data Consumers (“TDCs”), such as startups, enterprises, academic institutions and research organisations seeking access to datasets for AI model development. Data Collectives (“Data Collabs”) facilitate the aggregation, standardisation and coordination of datasets from multiple sources.
- Data Sharing Procedures are required to govern the sharing of datasets. Ministries, Departments and Organisations must establish procedures specifying dataset classifications as open, registered or restricted, consent mechanisms, de-identification standards, API access processes and penalties for misuse. Personal and sensitive data must not be shared in raw form and must undergo de-identification using pseudonymised keys retained by the originating agency. Shareable documents and datasets must be made available in machine-readable formats through APIs.
- Training Data Providers are responsible for data preparation, anonymisation and encryption. Before datasets are made available for AI training, TDPs must prepare and catalogue the datasets, remove personally identifiable information through anonymisation, encrypt the datasets and assign metadata describing their origin, sensitivity and access restrictions. Datasets must also be cryptographically tagged or watermarked to ensure traceability throughout the data-sharing lifecycle.
- Electronic Contracts regulate data access and usage. Training Data Consumers must submit formal requests identifying the intended use case. The Electronic Contract Management System validates these requests against the data-sharing policies prescribed by the TDPs or Data Collabs and the applicable governance requirements. This mechanism ensures that datasets are accessed only by authorised participants for specified purposes.
- AI model training takes place within Secure Data Environments. The framework provides for specialised, secure computational environments in which AI models are trained on sensitive and anonymised datasets without exposing raw data to external parties or Training Data Consumers. It also incorporates Federated Learning and Secure Multi-Party Computation to facilitate collaborative AI training across different data repositories without requiring the underlying datasets to be pooled.
- Differential Privacy and Zero-Trust Security mechanisms safeguard data confidentiality. Differential Privacy involves introducing calibrated statistical noise into query responses or model outputs to reduce the possibility of identifying individuals from aggregate results. The Zero-Trust Security Framework follows a “never trust, always verify” approach, requiring authentication and authorisation for every interaction, encryption of data at rest, in transit and during processing, security audits and monitoring of access logs.
- AI models undergo validation before deployment. AI models developed through the framework are subject to validation covering bias and fairness assessments, security and robustness testing, large-scale safety testing for high-risk applications and algorithmic explainability. Models must successfully complete the prescribed validation process before pilot deployment and subsequent scaling, in accordance with guidelines issued by the competent government authority.
- A multi-stakeholder governance and oversight mechanism ensures accountability. The governance structure comprises Training Data Providers, Training Data Consumers, Data Collabs, Technology Service Providers, sectoral experts and civil society representatives. Its responsibilities include participant registration and identity verification, registration of infrastructure providers, certification of AI models, management of electronic contracts, auditing of AI training workflows, compliance monitoring and dispute resolution. The competent government authority is empowered to suspend or revoke non-compliant activities.
- A phased implementation mechanism facilitates adoption across sectors. The framework provides for the establishment of pilot Data Exchange Platforms and Data Collabs in sectors such as healthcare and finance, regulatory sandboxes for AI training and testing, cross-border governance arrangements, awareness and capacity-building programmes and sustainable incentive mechanisms, including royalty and access-fee models for participating data providers.
- The framework facilitates sector-specific AI applications while safeguarding data privacy. The architecture enables data collaboration across healthcare, financial services, education and geospatial infrastructure. Its applications include AI-driven diagnostics, pharmaceutical research, fraud detection, credit-risk assessment, personalised learning and data-driven public services, while maintaining safeguards for personal data, commercial confidentiality and intellectual property.

Lexplosion Solutions
https://lexplosion.in/Lexplosion Solutions Private Limited is a pioneering Indian Legal-Tech company that provides legal risk and compliance management solutions through cloud-based software and expert services.